Modal Enhancements: Regional Routing, VM Sandboxes, Domain Allowlisting, and More
- Gate
- Machine Learning
- Departs
- Crew
- Robert Garcia
- Passengers
- 850
Modal introduces significant enhancements including regional routing for reduced latency, VM sandboxes for advanced workloads, and domain allowlisting for enhanced security.
Lower Latency with Regional Routing
Modal has rolled out a significant improvement aimed at reducing latency for its users. Functions can now be executed in various regions, specifically sending inputs through US West, EU West, or Asia Pacific South instead of defaulting to the US East region. This enhancement means that data is handled more efficiently, minimizing latency for requests made from outside the US East region. Additionally, it aligns with data residency requirements by keeping data within specified geographical boundaries.
The transition to regional routing can facilitate lower network latency, a key factor for applications requiring real-time responses. Users can adjust the settings of their functions with ease to enable this feature, enhancing performance across diverse deployments.
Read the docs for more information.
VM Sandboxes (Alpha)
Modal is excited to announce the introduction of VM Sandboxes, currently in the alpha phase. This new runtime operates on a real Linux kernel, allowing for the execution of workloads that operate Docker containers within the sandbox environment. It also supports essential Linux features including eBPF, systemd, cgroups, and custom filesystem mounts. This shift promises improved performance, particularly for I/O sensitive workloads, as the VM Sandboxes offer superior filesystem performance compared to traditional sandboxes.
Developers looking to leverage this feature can dive into the capabilities of VM Sandboxes through the provided documentation.
Check out our docs to get started.
Domain Allowlisting for Sandboxes
In a bid to improve security, Modal now allows users to restrict the domains accessible to processes within a Sandbox. By specifying a domain allowlist, users can better control external communications, as any attempts to connect to non-allowlisted domains will be blocked and logged. This feature reinforces security protocols, particularly vital in applications handling sensitive data.
outbound_domain_allowlist=[...] can be configured within the modal.Sandbox.create() method, thus ensuring that only approved domains are reachable from a specific sandbox.
For detailed guidance, learn more in the documentation.
Modal Skills Management
Modal users can now install and manage official Modal Agent Skills directly through the command line interface (CLI). This enhancement enables users to streamline their workflows by managing skills efficiently. The command modal skills install allows for easy access and implementation of these capabilities within applications.
Role-Based Access Control (RBAC)
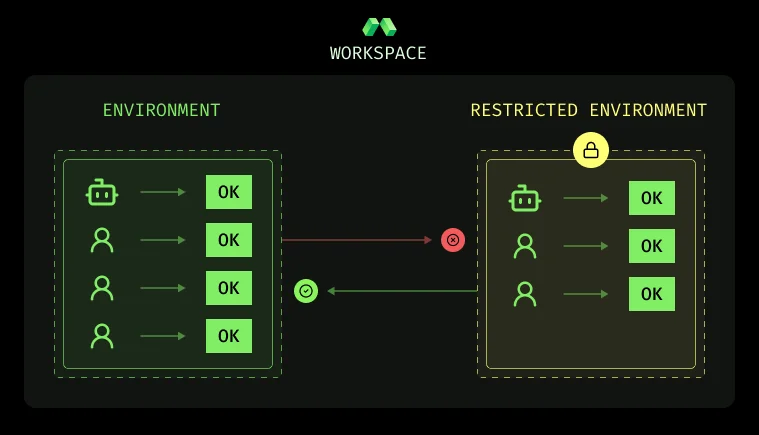
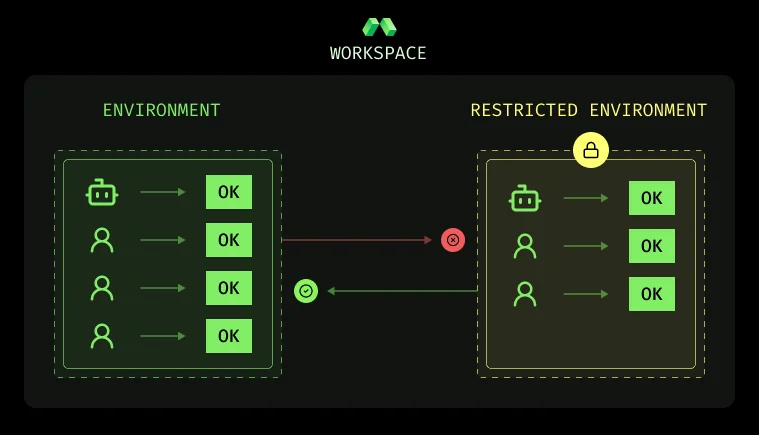
RBAC has been made available to Team and Enterprise plans, designed to enhance security by distinguishing access rights across different roles. By creating enforceable environments as boundaries, organizations can control access with precision. Restricted environments can be configured to be read-only by default, allowing for the precise scoping of secrets and applications to enhance security and auditability.
Access to modalities within environments can be meticulously logged, ensuring that all actions are traceable through Audit Logs. Developers interested in implementing RBAC can utilize the modal.Environment object alongside new features available in the modal environment CLI for code management.
For extensive information, read the blog.
Sharing Images with Named Images
Named Images provide a new capability to decouple image builds from application deployment or sandbox creation. This functionality simplifies the sharing of canonical images across multiple applications within the Modal environment. By serving as a Modal-native image registry, it enhances the way images are built and utilized within sandboxes, promoting consistency and efficiency.
Users looking to leverage this feature can find more details in the documentation: Learn more in the docs.
New Sandbox Features and Improvements
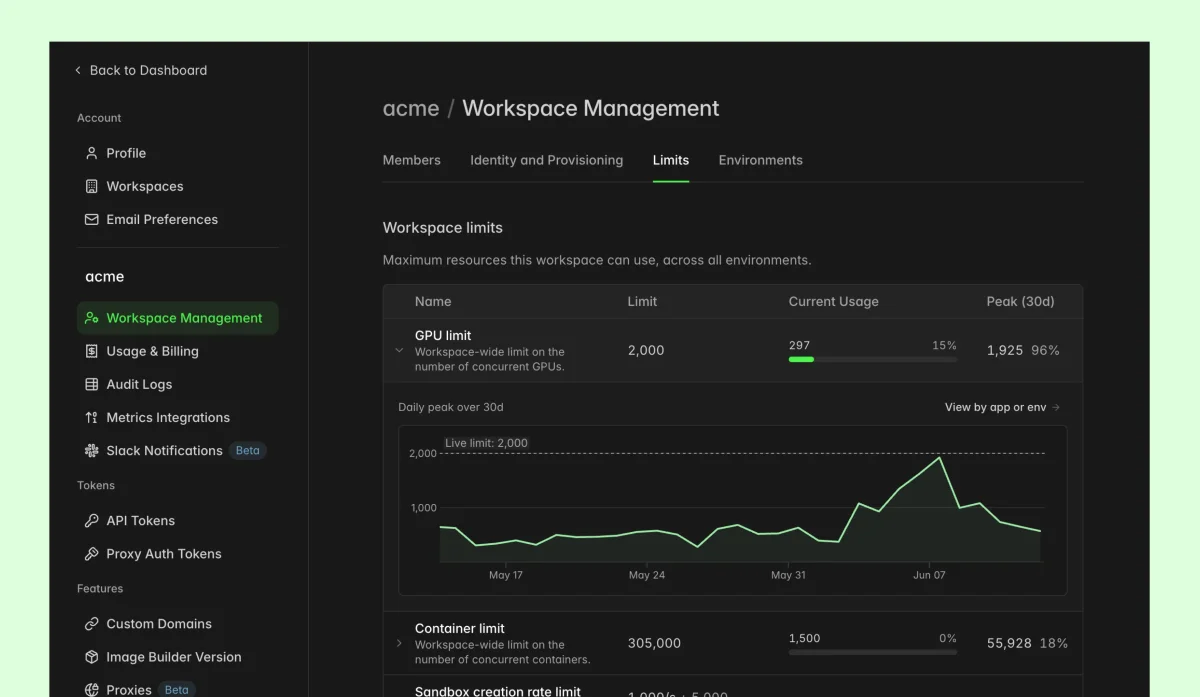
Modal has introduced several feature upgrades for sandboxes. Current workspace-wide GPU usage, container usage, and sandbox creation rates are now visible through a revised Workspace Limits UI. This insight can help users optimize resource allocation and monitor operations closely.
Moreover, Volume subdirectory mounts now allow users to scope a volume mount to specific subpaths, enhancing data management capabilities within sandboxes. This functionality provides granular control over read/write access, making it particularly useful for shared environments.
New readiness probes have also been released, enabling developers to monitor the initialization state of their applications without implementing manual polling mechanisms. This feature increases observability during the startup phase, providing essential insights into the timing of initialization processes.
The introduction of configurable TTLs for Sandbox Filesystem and Directory Snapshots empowers users to dictate how long snapshot states are retained, moving beyond fixed defaults. The default TTL for snapshots has been standardized to 30 days, although prior configurations can still be retained by specifying ttl=none.
SDK Updates
Modal has also released updates for its SDKs, including version 1.5.0 for the Python SDK and version 0.8.0 for both JS and Go SDKs. These updates typically include bug fixes, performance improvements, and possibly new features that enhance developer experience.
To stay updated on the latest changes, refer to the changelog.
Future Outlook
With these updates and enhanced features, Modal is clearly focused on enabling smoother operations for developers and researchers. The ability to manage resources, control access, and improve application performance are all significant steps towards optimizing the cloud-based development environment.


